---
title: "Automation of certificate ordering"
url: "https://help.internetx.com/en/api/processes-automation-of-certificate-ordering/"
lang: "en"
section: "API reference — API processes"
breadcrumb: "Certificate process automation"
updated: "2023-09-27"
---
# Automation of certificate ordering
Instructions für complete automation of the certificate ordering process. The QuickSSLPremium product is used here as an example and DNS is used as the authentication method.
The ordering process for S/MIME certificates differs and is described separately [here](/en/api/processes-automation-of-s-mime-certificate-ordering/).
## Basics of the JSON and XML API
All important information for the use of the JSON and XML API you can find in the [General API Basics](/en/api/core-general-api-basics/) and the [XML API Basics](/en/api/core-xml-api-basics/) and [JSON API Basics](/en/api/core-json-api-basics/). The specific [SSL objects](/en/api/core-ssl-objects/) are documented here, the [SSL tasks](/en/api/core-ssl-tasks/) here.
## Process overview
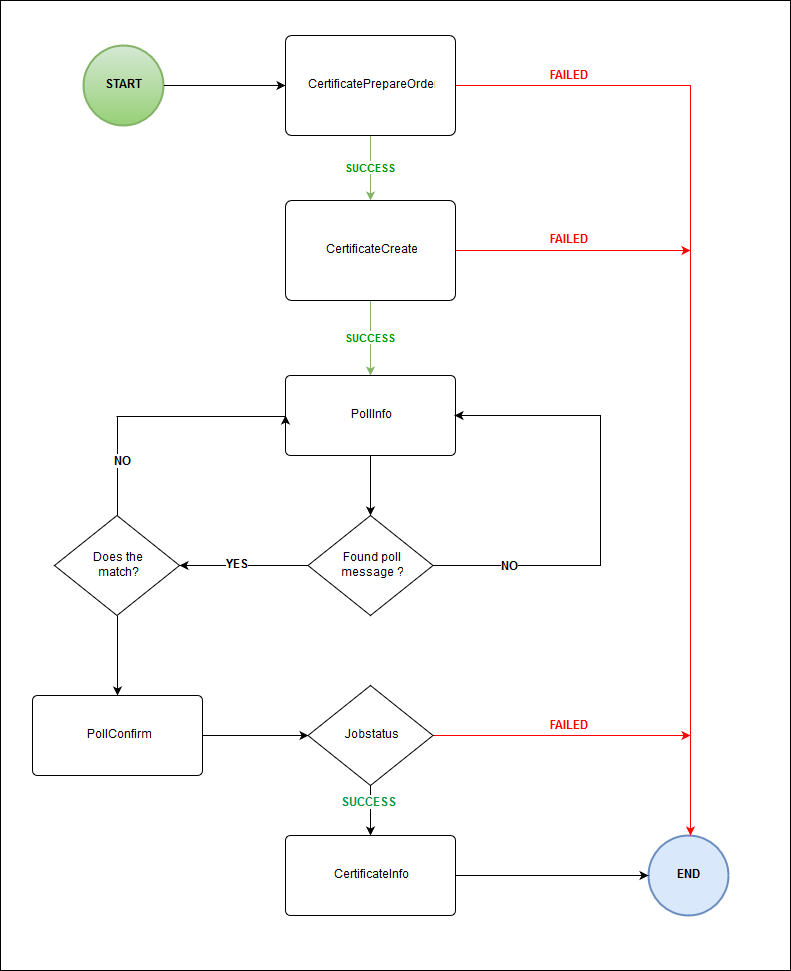
### Flow Chart
### Task names, codes and routes
| Task | Code | Route |
| --- | --- | --- |
| [SSLContactCreate](/en/api/core-certificate-contact-create/) | 400201 | POST /sslcontact |
| [CertificatePrepareOrder](/en/api/core-certificate-prepare-order/) | 400110 | POST /certificate/prepareOrder |
| [CertificateCreate](/en/api/core-certificate-create/) | 400101 | POST /certificate |
| PollInfo | 0905 | GET /poll |
| PollConfirm | 0906 | PUT /poll/$id |
| [CertificateInfo](/en/api/core-certificate-info/) | 400104 | GET /certificate/$id |
## DNS validation
DNS validation, i.e. validation by zone entry, is supported by many domain-validated certificates. To do this, for some CAs you must store a specific TXT or CNAME record in the zone belonging to the certificate name. This is checked for validity by the issuing certificate authority. If the corresponding zone is managed by InterNetX, the provisioning of the zone takes place automatically.
## Preparation
### Connecting SSLManager to AutoDNS
For the automatic provisioning of the zone, you have to connect the SSLManager to your AutoDNS access once. In the SSL Manager go to the **User Configuration** and click on the menu item **Connect SSL Manager to the Domain Administration System**.
Do not specify a protocol in the AutoDNS URL, e.g. no "http" or "https".
As Personal ADNS customer please specify the Personal ADNS ID (context), i.e. "[personaladnsid.login.autodns.com](http://personaladnsid.login.autodns.com)", all others use the URL "[login.autodns.com](http://login.autodns.com)".
The connection in the described way is possible only with AutoDNS X3 but not with AutoDNS Platform.
The connection with AutoDNS Platform is possible in the following way:
\- create an AutoDNS account
\- import the SSL Manager data. After the import the SSLManager account will be deactivated.
You will then be redirected to the AutoDNS login page. Enter your AutoDNS credentials here to establish the connection.
#### 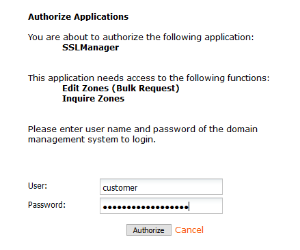
If necessary, you must enter the URL to your Personal AutoDNS or Registrar AutoDNS yourself.
Note that you must perform the following actions with your SSLManager user.
### Create contact
A technical and administrative contact is required to order a QuickSSLPremium certificate. You can use existing contacts or create new contacts. You can use the new contacts for future orders.
#### Contact create - example
```
POST /sslcontact
{
"fname": "John",
"lname": "Doe",
"phone": "+49-123-12345",
"fax": "+49-123-12345",
"email": "john.doe@example.com",
"title": "Admin",
"organization": "Company",
"address": [
"123 Main Street"
],
"pcode": "12345",
"city": "Anytown",
"country": "DE",
"state": "BY"
}
```
```
{
"stid": "20180926-stid",
"status": {
"code": "S400201",
"text": "Contact was created successfully.",
"type": "SUCCESS"
},
"object": {
"type": "contact",
"value": "100"
},
"data": [
{
"fname": "John",
"lname": "Doe",
"phone": "+49-123-12345",
"email": "john.doe@example.com",
"title": "Admin",
"organization": "Company",
"address": "123 Main Street",
"pcode": "12345",
"city": "Anytown",
"country": "DE",
"state": "BY",
"owner": {
"user": "user",
"context": 9
},
"id": 100
}
]
}
```
```
USERCONTEXTPASSWORD400201MichaelMustermann+49-941-1234560michael.mustermann@example.comAdminBeispiel GmbH
Maximilianstrasse 36000
93047RegensburgDEBayern
```
```
S400201Contact was created successfully.success20180926-app1-104
```
## Order a QuickSSLPremium certificate
### Create DNS record and check CSR
QuickSSLPremium certificates are verified by TXT entries. A new TXT record with specific values must be stored in the zone belonging to the common name (CNAME).
Example TXT :
example.com. 300 IN TXT "201704071405295z34is5g0jjairsdu0v5opdw8512td8kixzvtaacu4ebrkry5q"
With the _CertificatePrepareOrder_ task, the CSR key provided is checked for the correct bit length, for example, and the required authentication data is generated.
Note that the CSR code must be on a single line. Any existing line breaks must be removed.
#### Certificate prepare order - example
```
POST /certificate/prepareOrder
{
"plain": "----BEGIN CERTIFICATE REQUEST----- .... -----END CERTIFICATE REQUEST-----",
"product": "QUICKSSLPREMIUM"
}
```
```
{
"stid": "20180926-stid",
"status": {
"code": "S400110",
"text": "CSR key was checked successfully.",
"type": "SUCCESS"
},
"data": [
{
"plain": "-----BEGIN CERTIFICATE REQUEST----- ... -----END CERTIFICATE REQUEST-----",
"name": "example.com",
"keySize": 2048,
"countryCode": "DE",
"state": "BY",
"city": "Regensburg",
"organization": "Company GmbH",
"organizationUnit": "Entwicklung",
"product": "QUICKSSLPREMIUM",
"authentication": [
{
"method": "EMAIL",
"approverEmails": [
"admin@example.com",
"administrator@example.com",
"hostmaster@example.com",
"webmaster@example.com",
"postmaster@example.com"
]
},
{
"method": "DNS",
"dns": "example.com.\t\t300\tIN\tTXT\t\"201704071405295z34is5g0jjairsdu0v5opdw8512td8kixzvtaacu4ebrkry5q\""
},
{
"method": "FILE"
}
],
"algorithm": "RSA",
"signatureHashAlgorithm": "SHA256"
}
]
}
```
```
USERCONTEXTPASSWORD400110QUICKSSLPREMIUM
```
```
2048DEEntwicklungemail@example.comQUICKSSLPREMIUMDNSexample.com. 300 IN TXT "201704071405295z34is5g0jjairsdu0v5opdw8512td8kixzvtaacu4ebrkry5q"1FILERSASHA256S400110CSR key was checked successfully.success20170407-app1-223
```
### Ordering the certificate (certificate create)
With the _CertificateCreate_ task you send the actual order to the system. You must set certain values:
- Contact: Enter the contact ID of the required contacts. For QuickSSLPremium these are the administrative and the technical contact.
- Name: The name of the certificate.
- Product: The value for QuickSSLPremium is QUICKSSLPREMIUM
- Authentication: The generated authentication data
- Term: Specify a term allowed for the certificate. For QuickSSLPremium, this is 12 or 24 months.
- Software: select APACHESSL or IIS5
- CSR: The CSR that is part of the certificate
For the automatic provisioning of the zone, i.e. the automatic triggering of the zone update, it must be managed via AutoDNS and the SSL Manager and AutoDNS systems must be linked. See step Connect SSLManager to AutoDNS
#### Certificate create - example
```
POST /certificate
{
"adminContact": {
"id": 100
},
"technicalContact": {
"id": 100
},
"name": "example.com",
"lifetime": {
"unit": "MONTH",
"period": 12
},
"software": "APACHESSL",
"csr": "-----BEGIN CERTIFICATE REQUEST----- ... -----END CERTIFICATE REQUEST-----",
"product": "QUICKSSLPREMIUM",
"authentication": {
"method": "DNS",
"dns": "example.com.\t\t300\tIN\tTXT\t\"201704071405295z34is5g0jjairsdu0v5opdw8512td8kixzvtaacu4ebrkry5q\"",
"provisioning": true
}
}
```
```
{
"stid": "20180926-stid",
"status": {
"code": "N400101",
"text": "Certificate order was started successfully.",
"type": "NOTIFY"
},
"object": {
"type": "Certificate",
"value": "example.com"
},
"data": [
{
"id": 123456
}
]
}
```
```
USERPASSWORDCONTEXT400101100100example.comQUICKSSLPREMIUMDNSexample.com. 300 IN TXT "201704071405295z34is5g0jjairsdu0v5opdw8512td8kixzvtaacu4ebrkry5q"112APACHESSL
```
```
123456RUNNINGN400101Certificate order was started successfully.notify20180407-app1-334
```
### Receive notifications
The _CertificateCreate_ task automatically generates a request for ordering the certificate. Once the request has been processed, a notification is generated with information about the request. If the order was successful, you receive, among other things, the ID of the certificate ordered. The notification can be retrieved using the Polling and Push methods.
### Inquire certificate data
The _CertificateInfo_ task inquires the certificate data. The data can be queried and confirmed using the ID from the Checking and Confirming Notifications step.
#### Certificate info - Example
```
GET /certificate/$id
```
```
{
"stid": "20180926-stid",
"status": {
"code": "S400104",
"text": "Certificate data were inquired successfully.",
"type": "SUCCESS"
},
"object": {
"type": "Certificate",
"value": "example.com"
},
"data": [
{
"created": "2018-09-26T00:00:00.000+0200",
"updated": "2018-09-26T11:38:08.000+0200",
"id": 13258,
"owner": {
"user": "user",
"context": 9
},
"orderId": "2695961",
"adminContact": {
"id": 100
...
},
"technicalContact": {
"id": 100
...
},
"name": "example.com",
"lifetime": {
"unit": "MONTH",
"period": 12
},
"software": "APACHESSL",
"csr": "-----BEGIN CERTIFICATE REQUEST----- ... -----END CERTIFICATE REQUEST-----",
"server": "-----BEGIN CERTIFICATE----- ... -----END CERTIFICATE-----\n",
"serialNumber": "750C3006B23B90D0F396A3D153EB4C8",
"product": "QUICKSSLPREMIUM",
"expire": "2019-09-26T12:00:00.000+0200",
"authentication": {
"method": "DNS",
"dns": "example.com.\t\t300\tIN\tTXT\t\"201704071405295z34is5g0jjairsdu0v5opdw8512td8kixzvtaacu4ebrkry5q\"",
"provisioning": true
},
"certificateTransparencyPrivacy": "PUBLIC",
"domain": "example.com"
}
]
}
```
```
USERCONTEXTPASSWORD400104100
```
```
1003396954JohnDoe+49-941-1234560k.doe@example.comAdminExample GmbH
Maximilianstrasse 36000
93047RegensburgDEBayernUSERCONTEXTUSERCONTEXT203982017-01-01 10:35:222017-01-01 01:05:07JohnDoe+49-941-1234560j.doe@example.comAdminExample GmbH
Maximilianstrasse 36000
93047RegensburgDEBavariaUSERCONTEXTUSERCONTEXT203982017-01-01 10:35:222017-01-01 01:05:07example.com12APACHE2SERIALNUMBERQUICKSSLPREMIUMSHA22030-01-01 23:59:59ICA1DNSexample.com. 300 IN TXT "201704071405295z34is5g0jjairsdu0v5opdw8512td8kixzvtaacu4ebrkry5q"USERCONTEXTUSERCONTEXT1002017-01-01 00:00:002017-01-01 14:30:36S400104Certificate data were inquired successfully..success20181015-app1-672
```